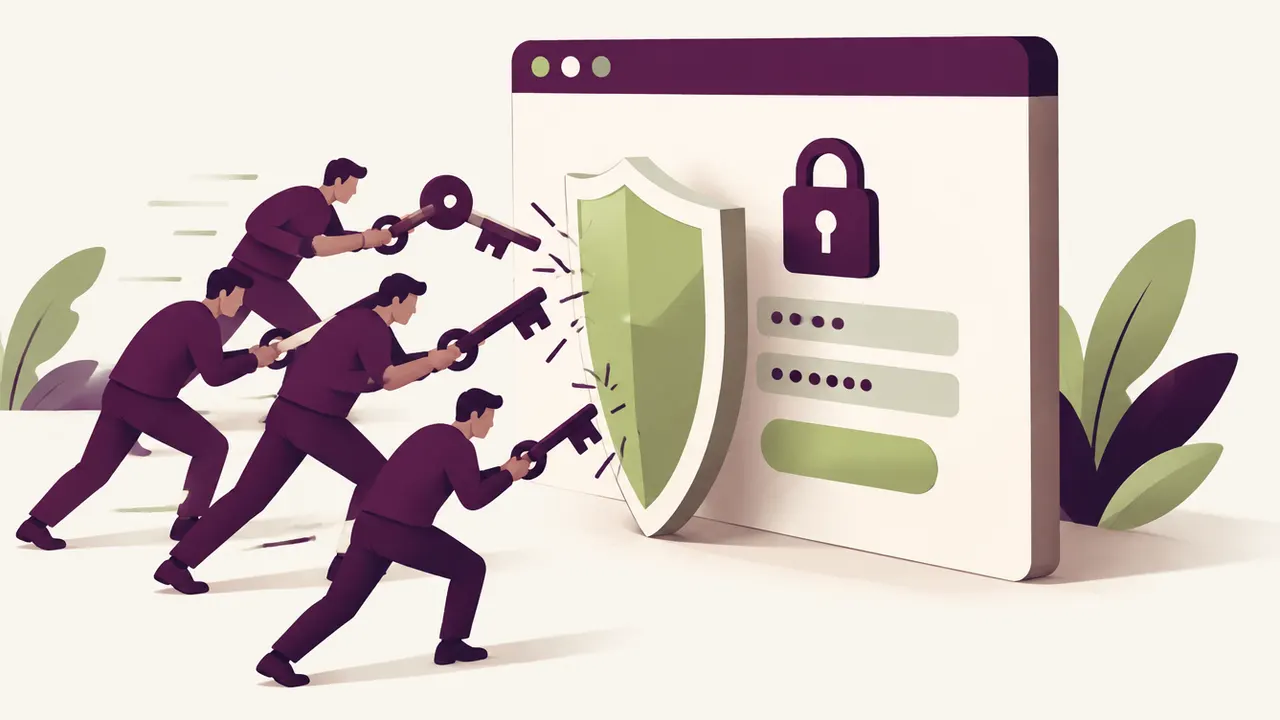
You open your hosting logs one morning and find hundreds, sometimes thousands, of failed login attempts overnight. That is the classic signature of a WordPress brute force attack: an automated script keeps testing combinations of usernames and passwords against your login page, hoping to eventually get one right.
This kind of attack does not target your business specifically. Bots scan millions of WordPress sites around the clock, looking for the weakest link: an "admin" username that was never changed, a password that is too simple, or a wp-login.php page freely reachable with no limit on attempts.
The problem is that these attempts sometimes pay off. A weak password will eventually give way against tens of thousands of tries, and the access gained is then used to inject malicious content, send spam, or redirect your visitors to other sites.
A WordPress brute force attack is countered by limiting the number of login attempts, enforcing strong passwords with two-factor authentication, and regularly monitoring access logs. These simple measures are enough to discourage almost every automated bot.
What a brute force attack actually is
There are two main variants. "Pure" brute force tries every possible combination of characters, which takes time but eventually works against a short password. Dictionary attacks, faster and therefore more common, test lists of passwords already leaked elsewhere or commonly used (123456, password, the company name followed by a year).
The most targeted entry points on a WordPress site are:
- the
wp-login.phppage, reachable by default to anyone who knows the address - the
xmlrpc.phpfile, a legacy interface that lets a bot test hundreds of passwords in a single request - direct access to
/wp-admin, which is automatically redirected to the login form
The signs that should raise a flag
An ongoing attack leaves traces you can spot if you know where to look:
- a sudden spike in failed login attempts in your host's logs
- the site slowing down during off-peak hours, often at night
- repeated alerts from a security plugin such as Wordfence
- an administrator account in the user list that you do not recognize
If you notice any of these signs without ever having set up protection, there is a good chance your site has been exposed for a while without you noticing. We cover the mechanics of these compromises in more depth in our article on why WordPress sites get hacked.
Best practices to block login attempts
A few settings are enough to make your site far less vulnerable:
- limit the number of login attempts with a dedicated plugin that temporarily blocks an IP address after a few failures
- enable two-factor authentication (2FA), which makes a stolen password useless on its own
- enforce long, unique passwords on every administrator account, not just your own
- disable XML-RPC if you do not use a mobile app or external service that relies on it
- rely on a web application firewall at the hosting level, which filters suspicious traffic before it ever reaches WordPress
These measures stack well together: each one closes a different door, and combined they make the attack far too costly in time for an automated bot to bother with.
Should you change the default login URL
Renaming wp-login.php to a custom address does not make your site unbreakable, but it removes it from the list of targets automatically scanned by the most basic bots. It is an extra layer of protection, to add on top of the previous measures rather than instead of them. Some security plugins offer this option in a few clicks, without touching WordPress core.
What to do if an attack is underway
If you notice an active attack, the priority is to stay calm and act in order:
- check that no attempt has succeeded, by reviewing the user list and the most recent logins
- block the most active IP addresses at the hosting or firewall level
- temporarily enable or tighten the login attempt limit
- change the passwords of every administrator account as a precaution
In most cases, a brute force attack fails and merely slows the site down slightly. But if you discover that access was actually gained, the situation changes: head to our guide on recovering a WordPress site after a hack.
When to call in a professional
If login attempts are running into the thousands every day, if your host is threatening to suspend your account for resource abuse, or if you simply are not comfortable configuring these protections, it is better to hand the matter to a professional. A quick audit confirms whether an intrusion has already taken place and puts durable protections in place instead of temporary patches.
Frequently asked questions
Can a brute force attack slow down my site even if it fails? Yes. Every login attempt consumes server resources. Thousands of attempts a day can be enough to slow your hosting down, especially on a shared plan, even without any access ever being obtained.
Is a plugin like Wordfence enough to fully protect me? It is an excellent first line of defense, especially for limiting attempts and detecting known threats. But it works best combined with strong passwords, two-factor authentication, and reliable hosting.
Should I worry if I see login attempts from other countries? Not necessarily on its own: these attacks are global and automated, they do not mean someone is specifically targeting you. That said, a high, sustained volume is a good reason to check your protections without delay.
Do you suspect an intrusion attempt on your WordPress site? Relax by Yumea secures your login page and checks whether any access ever succeeded. Describe your situation, the diagnosis is free.